
Securing a family office comes down to four pillars: governance with a named owner, layered cyber controls, physical protection that scales with the principal’s profile, and a rehearsed resilience plan. Family offices with more than $1 billion in assets under management reported high rates of cyberattacks, and most gaps trace back to a handful of fixable habits, not exotic threats.
Before anything else, do these three things this week:
- Enable multifactor authentication on every account tied to the office, including personal email for principals.
- Build (or update) a complete vendor inventory and flag which ones touch financial or personal data.
- Require dual-channel verification for any wire transfer or fund movement, no exceptions for “urgent” requests.
Key Takeaways
Family office security holds together only when governance, cyber controls, physical protection, and rehearsed resilience operate as one connected system rather than four separate budgets.
| Point | Details |
|---|---|
| Name an owner | Appoint a CRO or accountable security lead before adding new tools or policies. |
| Fix wire approvals first | Require dual-channel verification for every fund movement, with no exceptions. |
| Cyber and physical converge | Leaked travel data and compromised email routinely enable physical targeting. |
| Rehearse the response plan | Run annual tabletop exercises covering wire fraud, kidnap threats, and data leaks. |
| Global Security implements the program | Virtual Guard, executive protection, and training turn these controls into daily practice. |
Table of Contents
- Why Family Offices Have Become High-Value Targets
- Cyber Controls: What to Prioritize First
- Physical Security: Residences, Offices, and Travel
- Building Governance That Sticks
- Incident Response: The Plan You Actually Rehearse
- Who Should Implement This, and How
- What the Research Actually Tells Us
- Get Practical Protection Without Guesswork
- Sources
Why Family Offices Have Become High-Value Targets
Family offices sit at an unusual intersection: they hold institutional-scale wealth with the staffing and oversight of a small business. That mismatch is exactly what attackers exploit. North American family offices reported the highest cyberattack rates compared with offices in Europe and Asia Pacific, and the gap widens further with size. Offices managing more than $1 billion experience cyberattacks at a significantly higher rate than smaller ones.
Three vectors dominate:
- Phishing and social engineering aimed at finance staff or executive assistants who can authorize payments.
- Vendor compromise, where a third-party bookkeeper or IT contractor becomes the entry point.
- Ransomware targeting file servers holding tax, estate, and investment records.
These threats rarely stay digital. Attackers routinely mine leaked travel itineraries or compromised email threads to plan physical targeting, timing burglaries or confrontations to a principal’s known absence. A wire fraud attempt timed to a family’s overseas trip, or an email impersonating a trusted advisor requesting an urgent transfer, are not hypothetical scenarios. They are the two most common patterns investigators see.
Cyber Controls: What to Prioritize First
Technical defense for a family office does not require a Fortune 500 budget, but it does require sequencing. Here is the order that matters most:
- Multifactor authentication everywhere, with hardware security keys (not SMS codes) for principals and anyone with financial authority.
- Endpoint detection and response (EDR) on every device that touches office data, paired with automated patch management.
- Centralized logging so unusual access patterns get flagged instead of discovered weeks later.
- Network segmentation that keeps household IoT devices, smart locks, and staff Wi-Fi separate from the financial network.
- Identity governance, including quarterly access reviews and privileged account management for anyone touching bank portals.
- Vendor risk protocols: maintain a current vendor inventory, require security attestations, and limit what data each vendor can actually see. A guide like ShieldIQ’s vendor risk management framework offers a workable model for smaller offices building this from scratch.
- Mandatory phishing simulations, run quarterly, with role-based training for assistants and finance staff who handle payment requests.
- Secure communication channels for financial attachments and payment verification, replacing email threads with encrypted portals.
Phishing is the leading initial access point in wealth management, and successful incidents result in substantial financial costs on average. That figure alone justifies the training line item most offices try to skip.
Pro Tip: Give household staff and executive assistants their own segmented network access, separate from the principal’s financial systems. A compromised smart thermostat should never sit on the same network as the wire transfer portal.
Physical Security: Residences, Offices, and Travel
Digital controls only work if the physical layer matches them. Perimeter access management, professionally designed CCTV coverage, and periodic TSCM (technical surveillance countermeasures) sweeps for high-profile principals close the loop that phishing and social engineering try to open.
- Set access tiers for residences and offices so staff, vendors, and family members carry different credential levels.
- Schedule TSCM sweeps for principals with elevated public profiles or pending high-stakes negotiations.
- Vet executive protection teams directly, and confirm travel risk advisories before international trips.
- Insure high-value asset transport and follow documented vault standards for physical valuables.
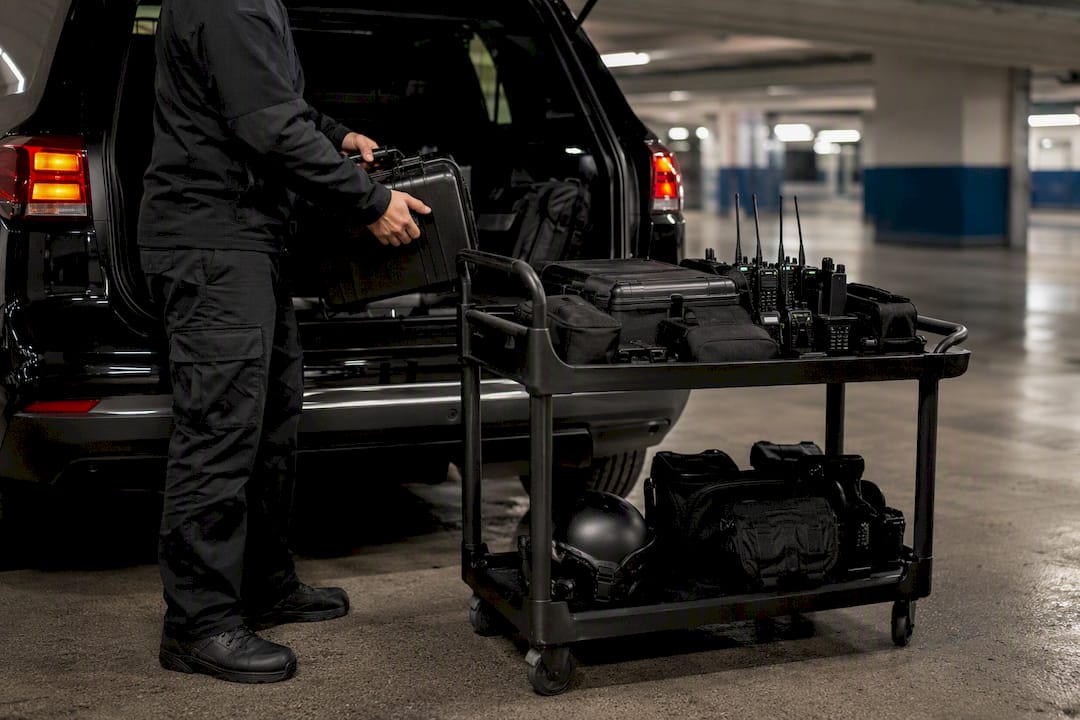
Roving vehicle patrols paired with remote video monitoring let an office maintain visible deterrence without staffing a guard post around the clock. When a monitoring system flags an anomaly, whether that is a triggered perimeter sensor or an unrecognized vehicle idling near a residence, the response needs to be physical and fast, not just a logged alert.
Pro Tip: Treat travel planning as a security function, not a scheduling task. Coordinate departure dates with your monitoring provider so residential coverage increases automatically while the family is away.
Building Governance That Sticks
Controls decay without ownership. Only about half of single-family offices express confidence in having a structured risk-identification process, and a notable portion indicate risk decisions do not reach the highest leadership levels. That gap is where most incidents actually originate.
- Appoint a Chief Risk Officer, or name an existing executive as the accountable security owner.
- Fold security reviews into the same cycle as investment committee and family council meetings.
- Document policies for wire transfer verification, data retention, vendor governance, and access lifecycle management.
- Set a recurring cadence: quarterly access reviews, annual tabletop exercises, and tracked incident response metrics.
A few maturity checks separate offices that talk about security from those that practice it:
- Vendor security attestations renewed annually, not signed once and forgotten.
- Cyber insurance policies reviewed against current threat coverage, not last year’s template.
- Third-party security assessments conducted on a fixed schedule rather than after something goes wrong.
The NIST Cybersecurity Framework gives smaller offices a usable structure for measuring where controls stand without hiring a full compliance team.
Incident Response: The Plan You Actually Rehearse
A significant portion of family offices lack an incident response plan, and only a minority describe their plans as robust enough to rely on. A plan that sits in a drawer is not a plan.
- Detect through logging and monitoring alerts, not employee guesswork.
- Contain by isolating affected systems and freezing suspicious transactions immediately.
- Communicate internally and, where required, to regulators, while protecting family privacy.
- Recover using backup access paths to critical accounts and alternate communication channels.
- Learn through a structured post-incident review that feeds back into policy.
Tabletop exercises should simulate the scenarios that actually happen: a fraudulent wire request during travel, a kidnap-and-ransom threat, or a large-scale data leak involving estate documents. Run one at least annually.
Pro Tip: Include the family principal in at least one tabletop exercise per year. Most incident response plans fail not because the policy is wrong, but because the principal has never practiced following it under pressure.
Who Should Implement This, and How
Alston brings a practitioner’s read on where family office security actually breaks down, drawing on sector data and the operational patterns seen across Global Security’s work with private clients. Global Security’s teams, built from law enforcement and military backgrounds, apply that same layered approach through Virtual Guard remote monitoring, executive protection, and hands-on training.
- Risk assessments that map both digital and physical exposure together, not separately.
- Remote monitoring and roving patrol coverage that scales with travel schedules.
- Executive protection and staff training built around real incident scenarios.
Offices with in-house IT can run the cyber checklist internally. Physical protection, executive protection, and integrated threat assessments generally call for specialists who do this daily.
| Point | Details |
|---|---|
| Ownership matters most | Name a CRO or security owner before adding new tools; unassigned risk decisions stall. |
| Cyber and physical are one problem | Leaked travel plans and compromised email routinely enable physical targeting. |
| Phishing is the biggest single cost | Average incident cost runs high, making training a priority investment. |
| Rehearse, don’t just document | Annual tabletop exercises expose gaps that written plans miss. |
| Global Security offers the implementation path | Virtual Guard, executive protection, and training give offices a practical way to operationalize these controls. |
What the Research Actually Tells Us
Most family office security advice treats governance as paperwork: a policy binder, a signed attestation, a checkbox on an annual review. The numbers say otherwise. Nearly a third of risk decisions never reach senior leadership, and close to a third of offices have no incident response plan at all. That is not a documentation gap. It is a decision-making gap.
The conventional advice, tighten passwords, buy better cameras, misses the actual failure pattern. Attackers do not choose between digital and physical avenues; they use whichever is open. A leaked itinerary becomes a break-in. A compromised email becomes a wire fraud. Treating these as separate budget lines, owned by separate people, is how offices end up with strong locks on one door and none on the other.
Prioritize the boring fix first: dual-channel verification on every fund movement, no exceptions for principals. It stops more fraud than any single technology purchase, and it costs nothing to implement this week.
— Alston
Get Practical Protection Without Guesswork
Global Security turns the four pillars covered in this article into an actual operating program instead of a policy document nobody reads. Where most firms hand you a report and walk away, Global Security’s teams, staffed by former law enforcement and military professionals, build the layered response themselves: Virtual Guard remote monitoring that flags anomalies in real time, roving patrols that respond to them physically, and executive protection for principals who travel with elevated exposure.
If your office needs a starting point, a risk assessment that maps digital and physical exposure side by side is the fastest way to see where the actual gaps sit. Get in touch through Global Security’s services page to schedule an assessment, or explore executive protection options directly if travel security is the immediate concern.
Sources
- The Family Office Cybersecurity Report, 2024 (Deloitte excerpt)
- How to manage risks and protect family offices (EY)
- Why Wealth Managers Are Cybercriminals’ Favorite New Target (Kiteworks, 2026)
- Family offices face rising risk in the gaps between cyber and physical security (Sikich)